
0Day: CVE & Exploit Alerts
Richard Lous Developer Tools iPhoneiPadiPod touch
0Day: CVE & Exploit Alerts is a free Developer Tools app for iPhone and iPad by Richard Lous. Rated 5.0/5 from 2 ratings. Requires iOS 18.0.
- Rating
- 5.0
- 2 ratings
- Price
- Free
- on the App Store
- Size
- 10 MB
- Age 4+
- Updated
- Jul 21
- 2026 · v1.1.0
Screenshots



About 0Day: CVE & Exploit Alerts
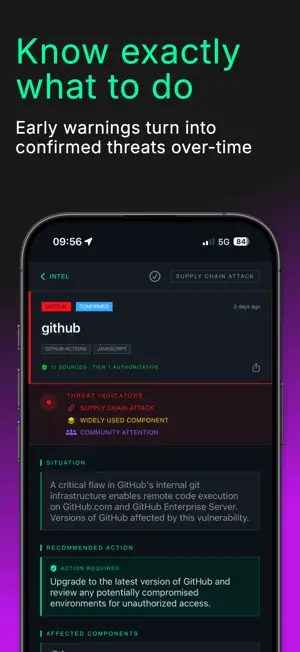
Most security feeds bury you in CVEs that have nothing to do with what you ship. 0Day cuts through that. Zero-days, supply chain attacks, compromised packages, active exploits: filtered to your exact stack, the moment they break. Pick your stack once during onboarding: npm, PyPI, Docker, Kubernetes, React, Rails, OpenSSL, whatever you use and the feed shows you only what touches your tech. No noise. No irrelevant advisories. Just what matters to you. The goal is lead time. Know about a compromised package, a poisoned build pipeline, or an actively exploited CVE before it reaches your CI, your production deployment, or your customers. Before the news cycle. Before the stragglers patch. Before you're the one scrambling at 2am. WHY 0DAY - Privacy-first — no analytics, no tracking, no third-party SDKs - Early warnings before the news cycle — the moment a threat breaks, you know - Stack-aware filtering — see only threats that hit the tools you use - Multi-source corroboration — duplicates merged, sources ranked by tier - Curated, not firehose — every alert is tied to a specific component - Full archive — searchable history of every threat that hit your stack HOW IT WORKS Every item in the feed goes through a three-stage lifecycle so you can tell the difference between "we're watching this" and "this is real, act now": CANDIDATE — A single source has reported an incident. In the pipeline, being correlated, not yet corroborated. EARLY WARNING — Either an authoritative research outlet flagged it, or a second independent source has confirmed the same incident. Pushed to your device immediately — this is the lead time the product is built for. CONFIRMED — Two or more authoritative sources agree, or three independent sources total. High-confidence state you can act on without double-checking. INSIDE THE FEED Each alert gives you a plain-English summary, affected components with version ranges, recommended action, CVE and GHSA identifiers with tappable links to the upstream advisories, and a timeline of when each source reported the incident. PRIVACY We collect only what we need to run the service: your email for sign-in, your stack selections, your notification preferences, and your device token for push delivery. No analytics. No crash reporting SDKs. No advertising identifiers. No cross-app tracking. All data is stored in the European Union on AWS infrastructure. You can delete your account and all associated data instantly from Settings. SUBSCRIPTION 0Day Pro unlocks the full experience: early warning alerts, push notifications, full archive access, remediation guidance, and stack filtering. All new users get a free 14-day trial — no payment required to get started. After the trial, subscribe to keep full access. Offered as a monthly or annual subscription. Payment is charged to your Apple ID at confirmation of purchase. Subscription auto-renews unless cancelled at least 24 hours before the end of the current period. Manage or cancel anytime in iOS Settings → Apple ID → Subscriptions. Terms of Use: https://0day.lous.nl/terms Privacy Policy: https://0day.lous.nl/privacy
What’s new
Version 1.1.0 · Updated July 21, 2026
- Updated Terms and Privacy URLs - General bug fixes
App privacy
The developer, Richard Lous, reported these privacy practices to Apple.
Data Used to Track You
The following data may be used to track you across apps and websites owned by other companies:
- Identifiers: User ID
Data Linked to You
The following data, which may be collected and linked to your identity, may be used for the following purposes:
- Contact Info: Email Address, Name
- Identifiers: User ID
Used for: App Functionality
Data Not Linked to You
The following data, which may be collected but is not linked to your identity, may be used for the following purposes:
- Identifiers: User ID, Device ID
- Usage Data: Product Interaction
- Diagnostics: Crash Data, Other Diagnostic Data
Used for: Analytics
Alternatives to 0Day: CVE & Exploit Alerts
Looking for apps like 0Day: CVE & Exploit Alerts? Here are 6 similar apps on the App Store. The highest rated is DNS Toolkit (5.0/5), and 5 of the 6 are free to download.
-
 DNS Toolkit
5.0
-
 PocketShell
-
 SSL Checker & Expiry Monitor
-
 DevBuddy Dev Tools
-
 ByteSniffer
-
 DevTools+: Dev Tools & Code
| App | Rating | Price | Last updated | Compare |
|---|---|---|---|---|
| 0Day: CVE & Exploit Alerts | 5.0 / 5 (2 ratings) | Free | July 21, 2026 | |
| DNS Toolkit | 5.0 / 5 (2) | 1.99 USD | Sep 8, 2025 | Compare |
| PocketShell | – | Free | Jul 3, 2026 | Compare |
| SSL Checker & Expiry Monitor | – | Free | Oct 6, 2026 | Compare |
| DevBuddy Dev Tools | – | Free | Mar 24, 2026 | Compare |
| ByteSniffer | – | Free | Sep 16, 2026 | Compare |
| DevTools+: Dev Tools & Code | – | Free | Sep 9, 2026 | Compare |